As cyber threats evolve rapidly in 2026, Australian SMEs must build stronger defenses. The ASD Essential Eight framework offers practical, plain-language strategies to achieve this starting at Maturity Level One. Adopting these foundational measures can dramatically reduce risk and improve resilience.
The ASD Essential Eight is a prioritized set of mitigation strategies designed to protect businesses against common cyber attacks. For SMEs, beginning at Maturity Level One means implementing basic but effective controls such as application whitelisting, patching applications, and restricting administrative privileges. For example, ensuring all software is regularly updated prevents exploitation through known vulnerabilities. This systematic approach helps SMEs build cybersecurity maturity incrementally without overwhelming resources or expertise.
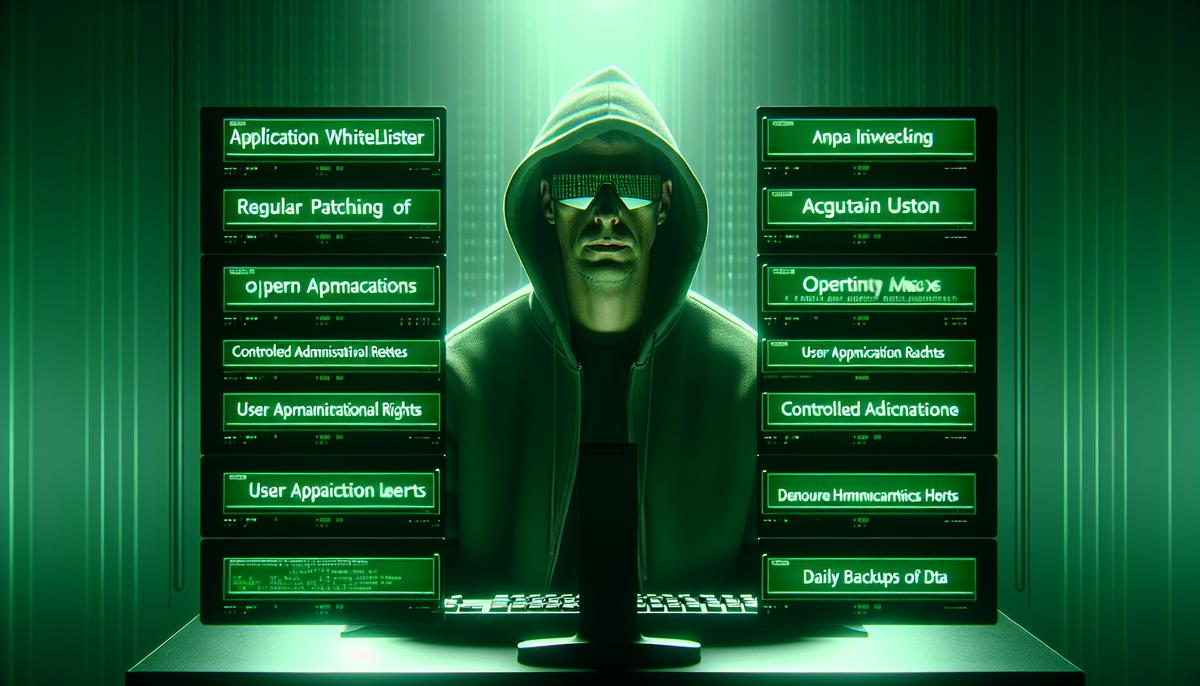
• Start with application whitelisting to reduce malware risks.• Patch applications and operating systems regularly to close security gaps.• Control administrative rights to limit potential damage from attacks.• Enable user application hardening to reduce attack surface, e.g., disabling unnecessary office macros.• Daily backup of critical data safeguards business continuity in case of breaches.
The trend towards measurable cybersecurity maturity models empowers SMEs to prioritize efforts and budget efficiently. Experts agree that clear, understandable frameworks like the Essential Eight are crucial for demystifying cybersecurity. As cybercrime grows more sophisticated, businesses that adopt foundational strategies first can better protect assets and client trust. The framework’s practical guidance aligns with global best practices while being tailored for smaller enterprises.
How are you applying the ASD Essential Eight in your organization? Share your experiences or challenges in implementing these strategies at Maturity Level One. Let’s connect and discuss how SMEs can continuously strengthen their cybersecurity posture in 2026 and beyond.
#CyberSecurity #ASDEssentialEight #SMEs #RiskManagement #CyberResilience